Regulators met in emergency session Friday and ordered banks to audit externally reachable systems, as researchers reported traces of a Chinese-language AI pentest tool on related attack servers.
The company says it has secured the 13 million-follower @Microsoft handle and will take legal action over use of the Clippy brand, but has not said how attackers got in.
FedEx and UPS were the most-named targets in 85 criminal forum records, where buyers offered per-task fees, escrow and even schemes to get recruits hired.
Proofpoint says the group built rapport with fake advisory-committee and Senate report invitations before steering targets to pages that captured Microsoft 365 logins and sessions.
The designations target the first fugitive on the FBI's Ten Most Wanted list sought for cybercrime, along with associates, Mexican companies and TRON wallets tied to Tren de Aragua.
South Korea’s financial watchdog opened an emergency inspection after the lender reported that an outside party bypassed authentication on a loan-broker platform.
Leaked npm tokens were almost all dead, but more than half of exposed Google Cloud service account keys still worked, the researchers found.
Researchers tested 21 vehicles and 30 companion apps with Consumer Reports and found that using a carmaker's app roughly doubles exposure to ad and tracking firms.
Lures posing as Zoom installers, Acrobat updates and DHL notices delivered MSP360 RMM, which then pulled in ScreenConnect as a second remote channel.
A shared backup format means message history can now move between Android, iOS and desktop, protected by a recovery key that attackers are already hunting.
While stationed at Dover Air Force Base, the pair phished employee logins and rerouted payments, including a $1.7 million transfer from an Iowa City victim.
The bureau's cyber chief addressed the extortion crew directly in a video, and Director Kash Patel confirmed U.S. agents helped Dutch police make this month's arrest.
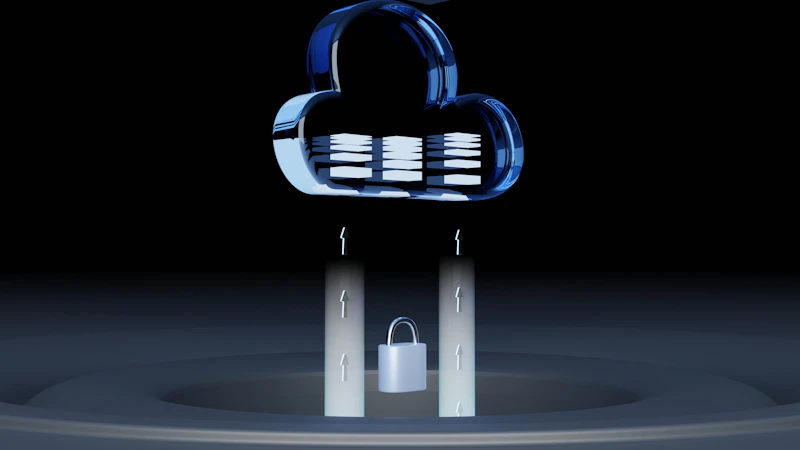
A new zero-retention option sends safety-flagged API content to the customer's own cloud bucket, where only an attested runtime can decrypt it for review.
A Rotterdam court ordered the 24-year-old, a previously convicted hacker working in security, held for at least 90 days as police pursue two separate cases.
Huntress traced at least 40 infections to a lure that began with a sponsored Google result and a Custom GPT hosted on chatgpt.com.
Buying an established GlobalSign root gives Cloudflare instant device reach while it pushes compact Merkle Tree Certificates for a post-quantum web.
AT&T Ventures led the round, which more than doubled the New York startup's valuation in seven months as agent-security vendors multiply.
The Tel Aviv startup, led by a former Wiz engineer, uses an endpoint sensor to tell when an AI agent rather than an employee is acting under a login.
A Times review of leaked samples found family contacts, PreCheck-linked IDs and counterintelligence postings, and an internal memo assumes every employee is affected.
The verdict covers claims about privacy controls, data sales and post-Cambridge Analytica app reviews, and a judge will now set penalties of up to $5,000 per violation.
Cleafy found about 100 deployments of the malware-as-a-service console since April, with its newest version asking Gemini to rank infected phones.
Two compromised service principals, one with credentials left in a public GitHub issue, were enough to delete resources across more than 100 storage accounts in about seven minutes.
Titan never checked JWT signatures, so a forged admin token opened a public SQL endpoint to 17 databases holding an estimated 17.3 trillion rows.
Sold for $200 to $950, the kit bundles DDoS tools, an infostealer and a mode that burns through victims’ paid AI API quotas.